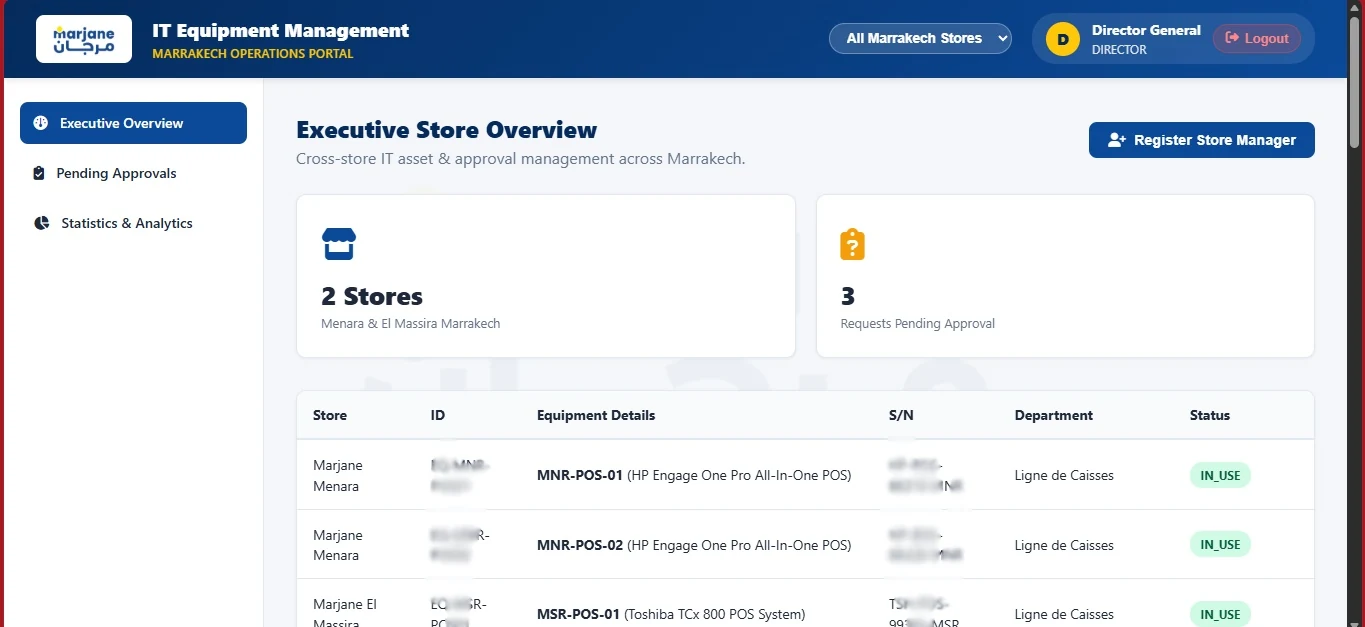
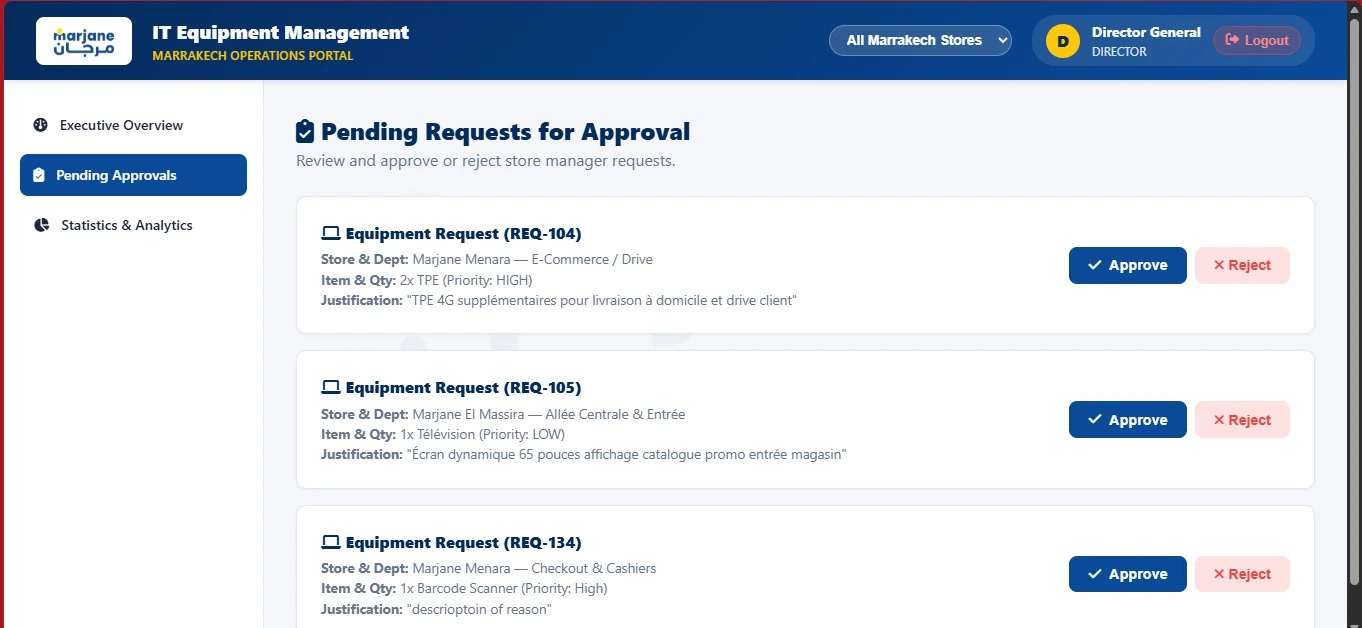
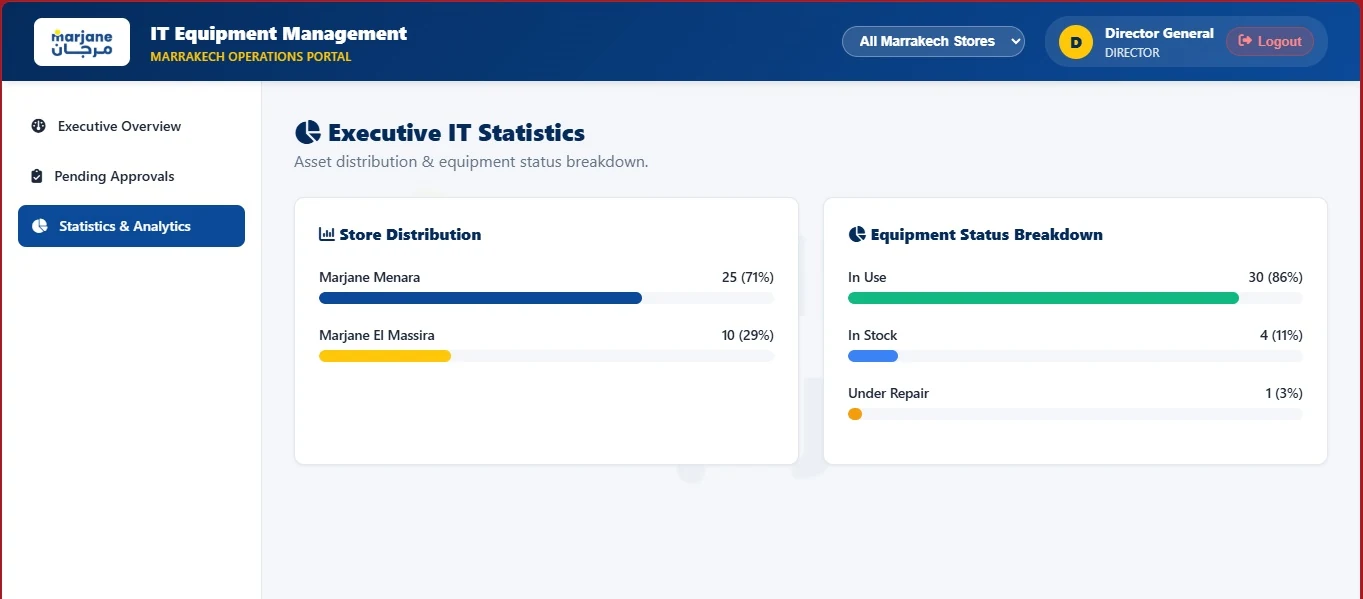
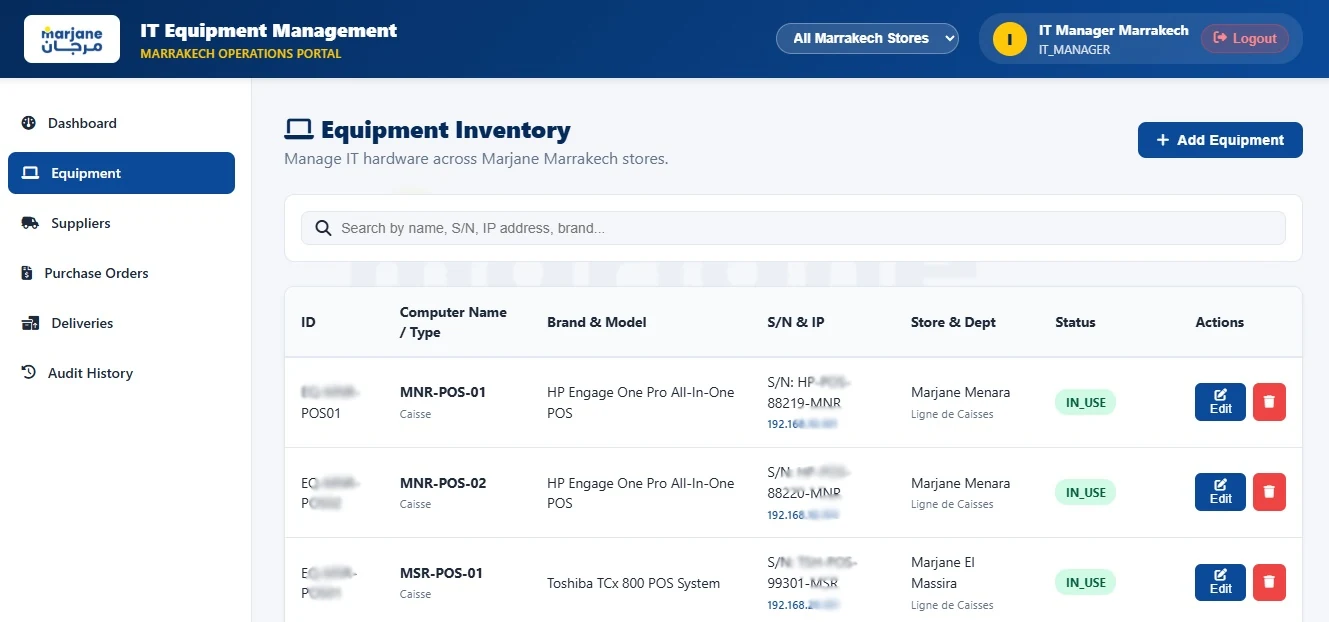
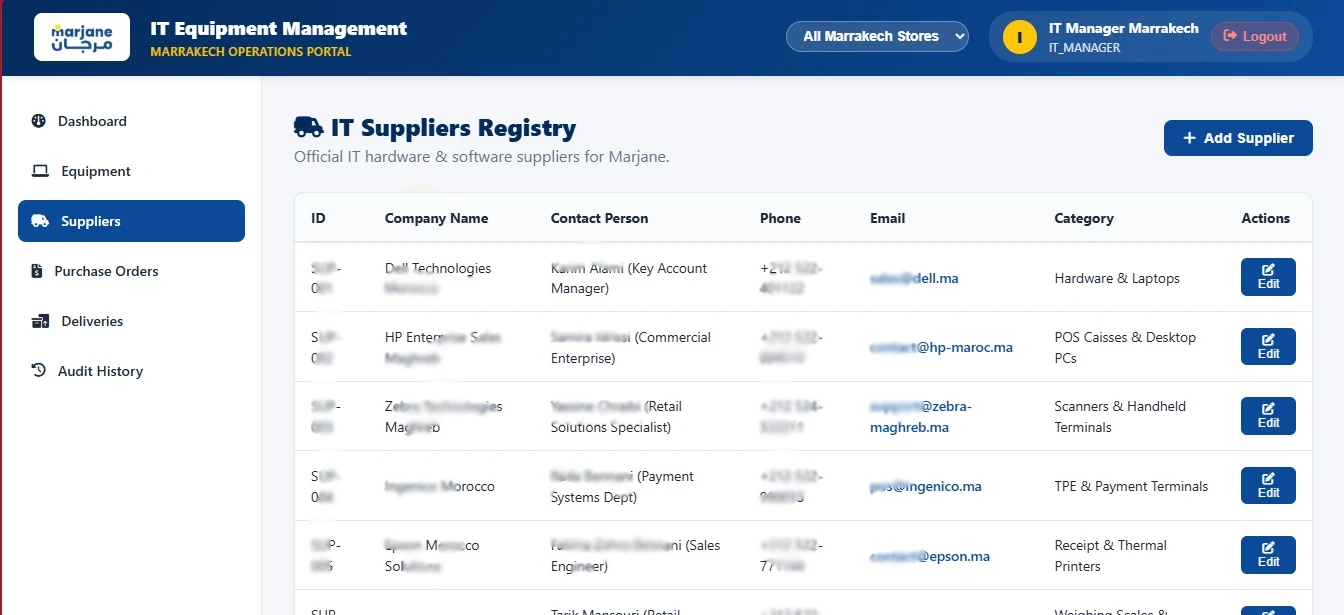
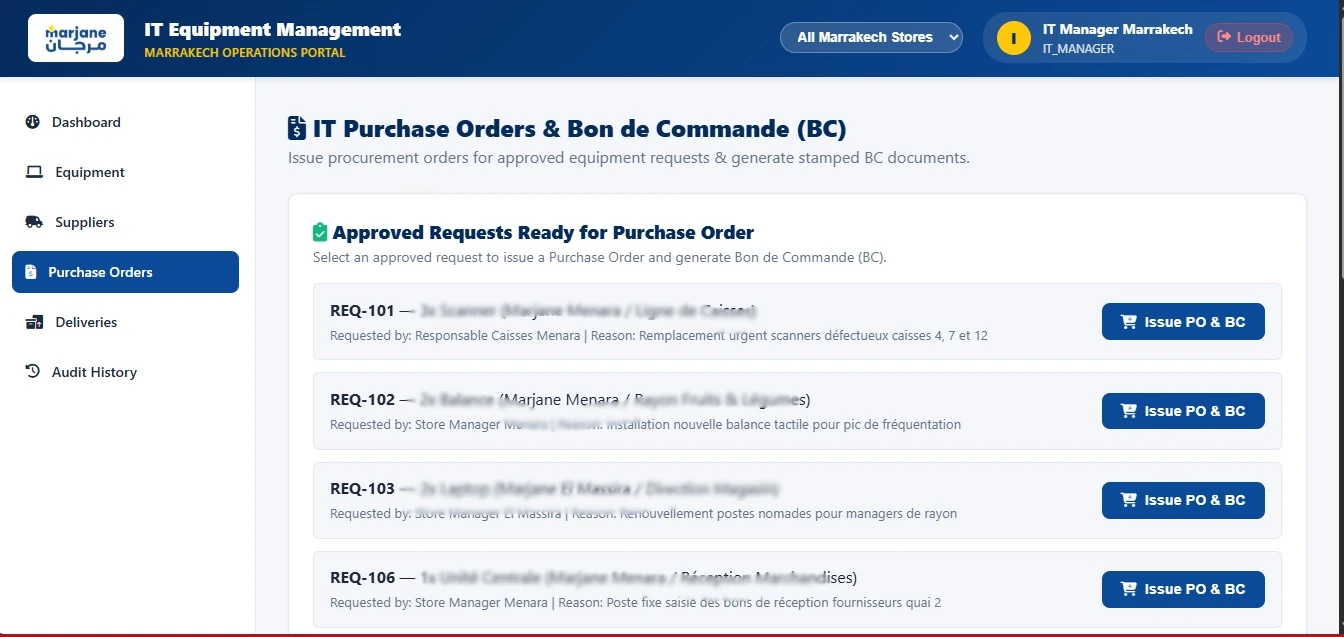
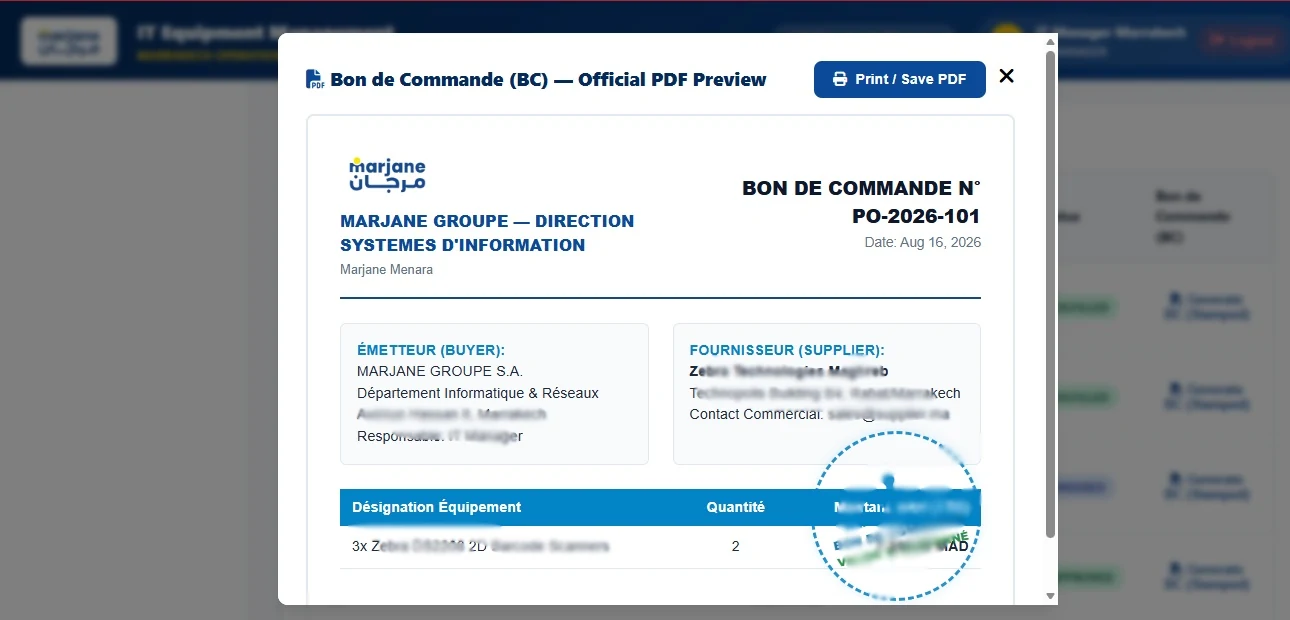
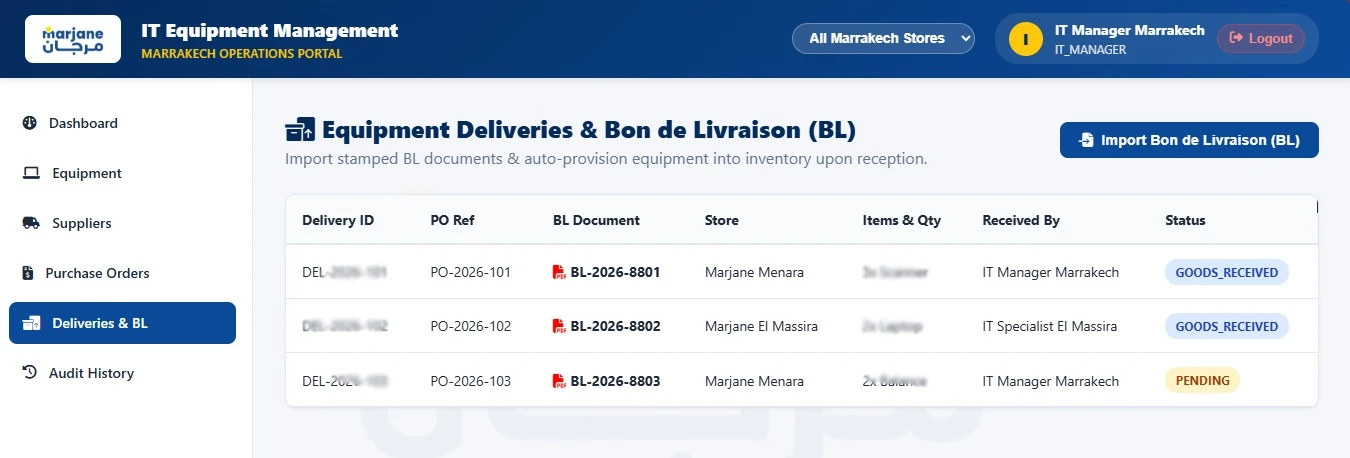
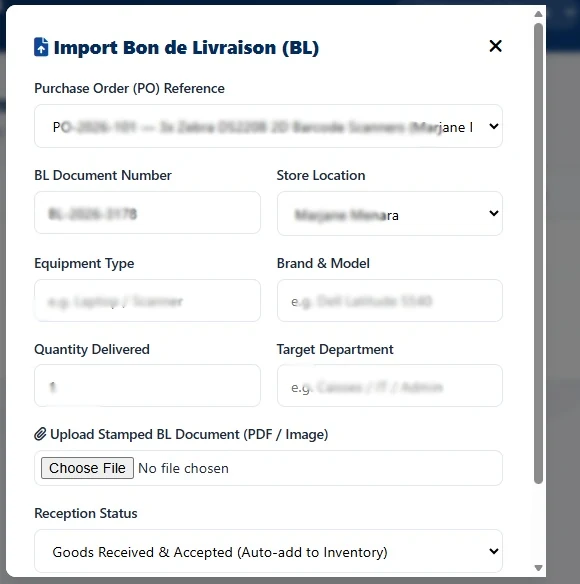
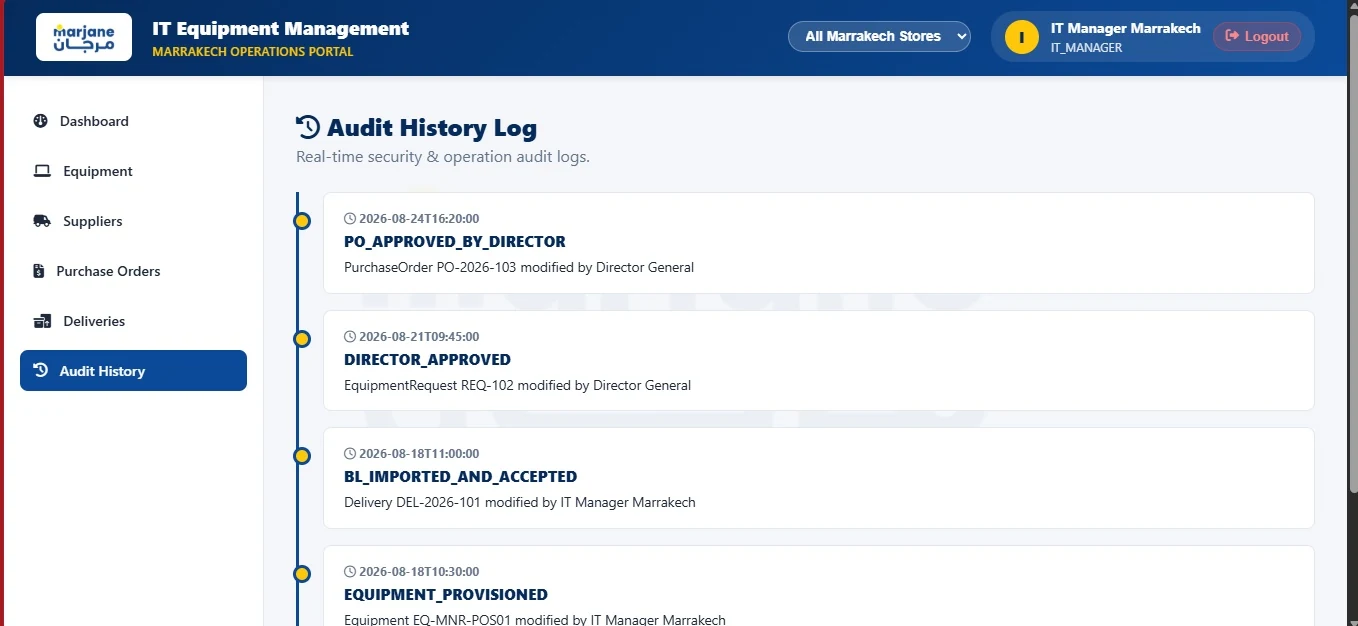
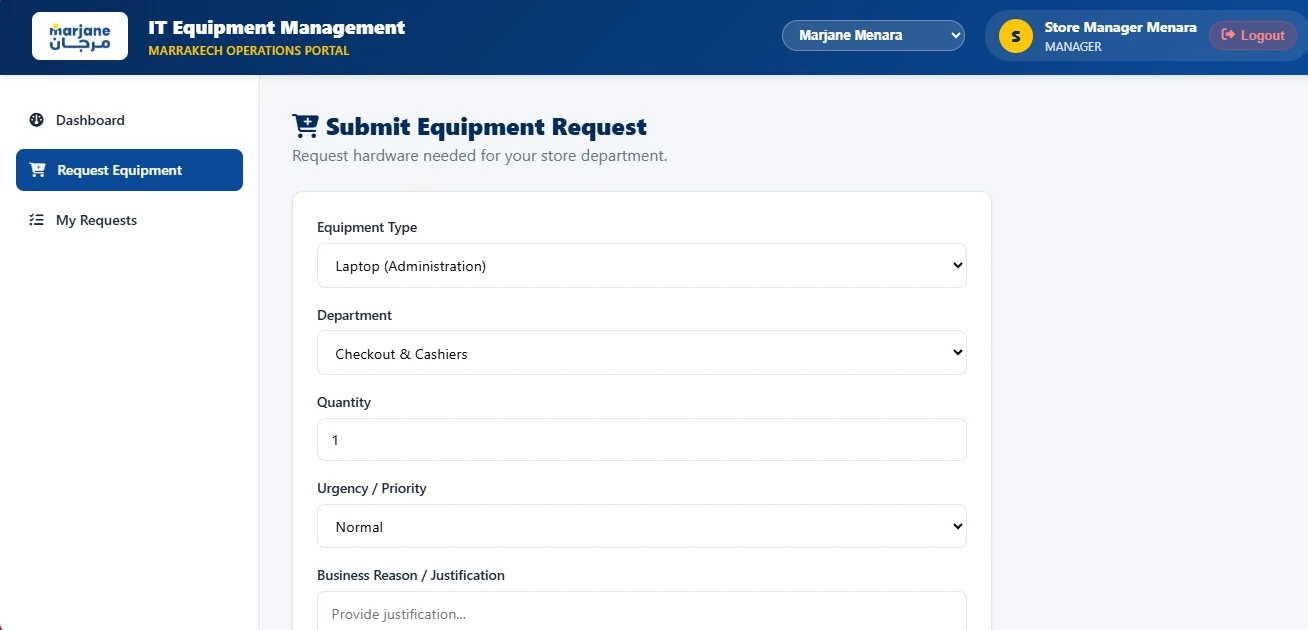
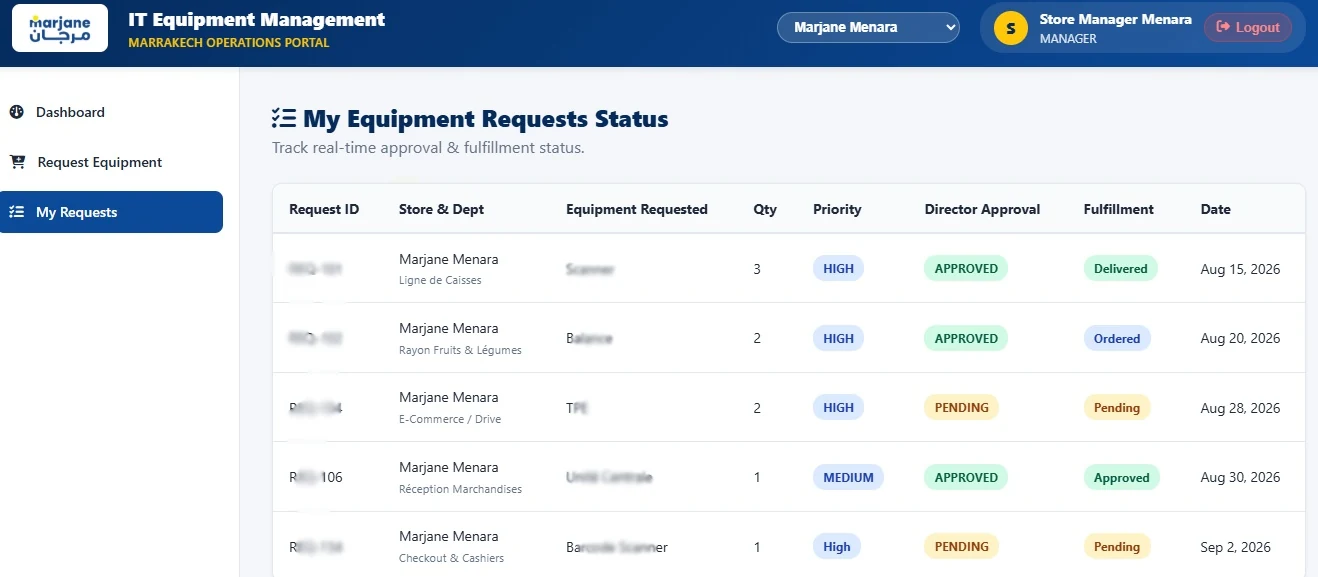
With my team, I helped build an internal platform to digitalize IT equipment management (requests, approvals, purchase orders, deliveries).
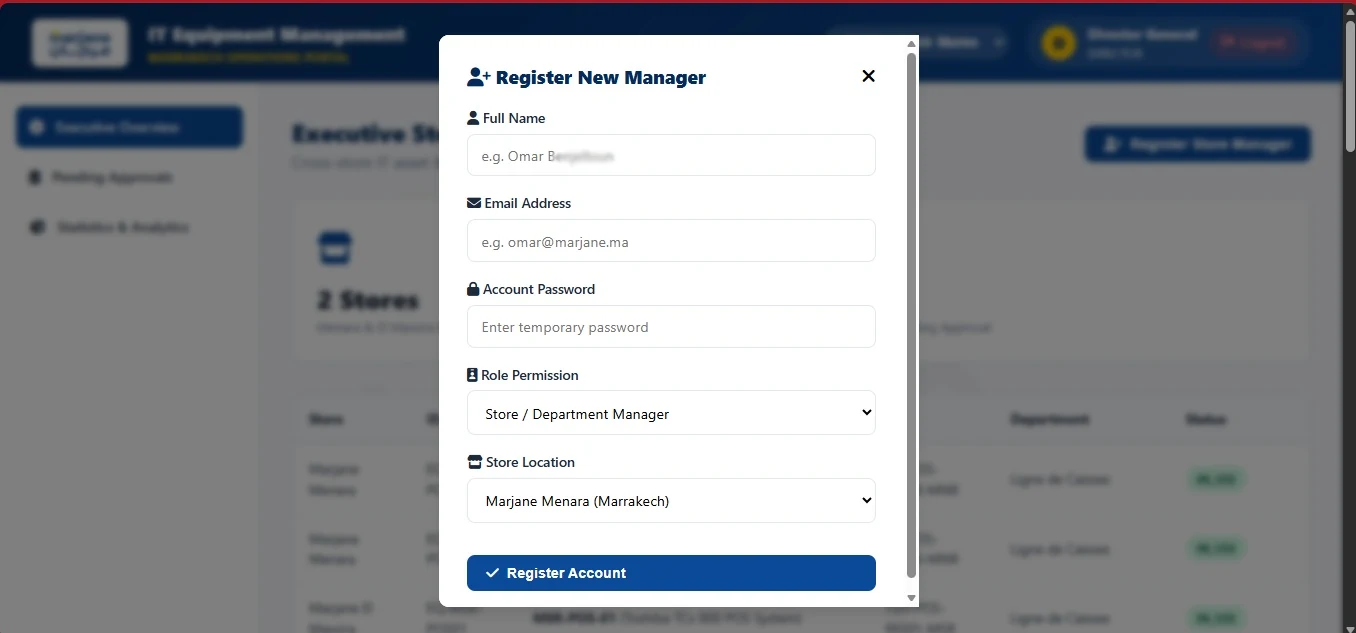
I worked on the Spring Boot API side, adding authentication and role-based access (so each user only sees and does what their role allows).
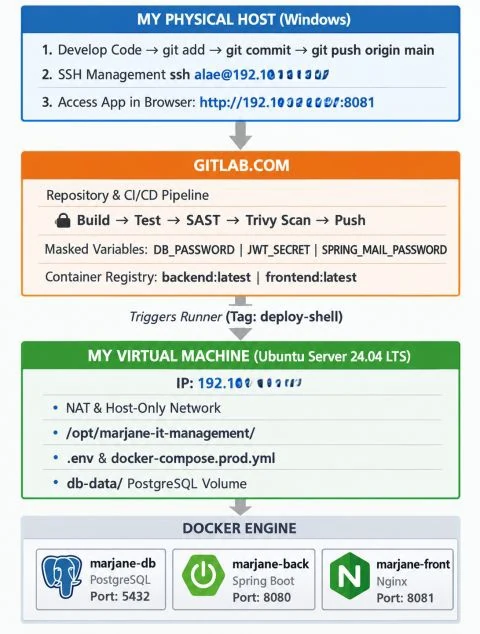
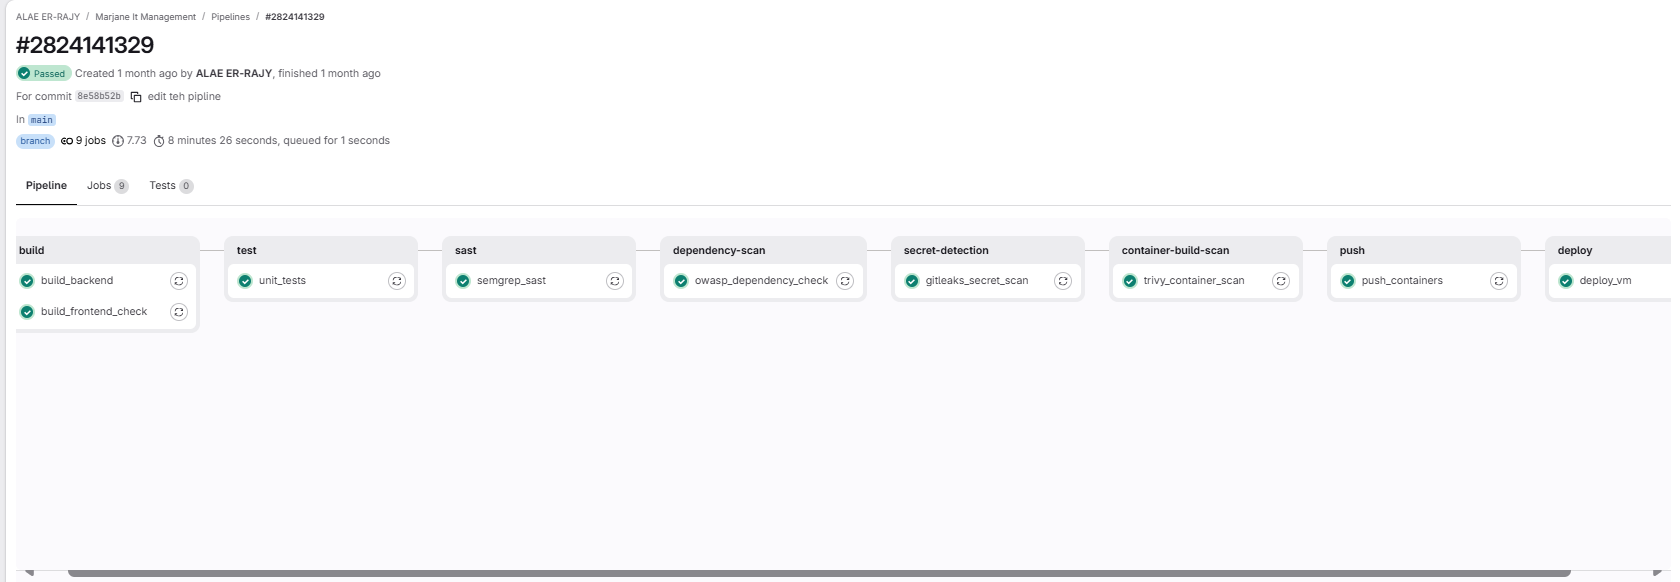
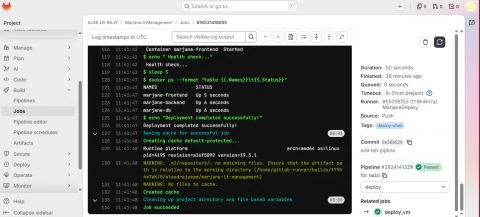
I also set up the DevSecOps part: a GitLab CI/CD pipeline with SAST (Semgrep), dependency scanning (OWASP Dependency-Check), secret detection (Gitleaks), and container scanning (Trivy) — deployed with Docker on an Ubuntu server with zero-downtime rollout.